I have one practical question for you: does your online store sell just as well in a calm week as in a week when everything around it is shaking?
Instability comes from different directions: sometimes as a dispute over institutions, sometimes as a cloud outage on the other side of the world. Nobody asks your store for its opinion. Fortunately, most of these situations call for the same, fairly boring precautions.
Regulation changes faster than stores do
Let’s start with the law, because it changes most often. Grant Thornton counted 12,400 pages of new law in Poland in 2025, the fewest in 19 years1. The first half of 2026 alone added another 5,287 pages, around 43 pages for every working day2.
Businesses feel it. In a 2025 Grant Thornton survey, 53% of companies said the law changes too often, and 85% of those said this makes running their business significantly harder3.
Uncertainty reaches institutions too. The latest example is the dispute around Poland’s Constitutional Tribunal: at the end of October its longest-serving judge ordered a one-month break in the duties of the Tribunal’s president and vice-president and called a general assembly of judges for 3 November4. It is not for me to judge who is right. For a store, what matters is simpler: the less predictable the surroundings, the more it pays to be ready for change early.
For an online store, regulation means concrete changes to the code: new fields on the product page or a new integration. Look at the last two years:
- January 2024, KSeFPoland's Ministry of Finance cancelled the start of mandatory e-invoicing planned for 1 July 2024. An audit found critical errors in the project, and the new dates were set for 1 February and 1 April 20265.
- December 2024, GPSRA store selling at a distance must show the manufacturer's details, a photo and product identifiers next to each product8.
- June 2025, accessibilitySince 28 June 2025 online stores and shopping apps have had to meet accessibility requirements. Microenterprises providing services are exempt7.
- April 2026, NIS2Poland's amended national cybersecurity act has applied since 3 April 2026. Companies it covers had until 3 October to register and have until 3 April 2027 to comply6.
The KSeF story shows that statutory deadlines can move, while the store still has to be ready on the day the rule finally applies. You can read more about what KSeF changes in a store in our post on KSeF.
The outage comes from outside
What happens when everything in the store works and customers still can’t buy? Recent years offer plenty of examples:
- AWS, October 2025. A fault in DNS automation in the us-east-1 region took down part of Amazon’s services for around fourteen and a half hours, from the evening of 19 October to the afternoon of the 20th10.
- Cloudflare, November 2025. An oversized configuration file crashed the proxy servers that carry its customers’ website traffic. Problems began at 11:20 UTC and were fully resolved at 17:0611.
- CrowdStrike, July 2024. A faulty security software update took down around 8.5 million Windows machines12.
- OVHcloud, March 2021. After a fire at its Strasbourg data centre, around 3.6 million websites went offline13.
Cloudflare put its own outage plainly:
Today was Cloudflare’s worst outage since 2019. Cloudflare, post-mortem of the 18 November 2025 outage
The Uptime Institute looked at nine years of outage data. Around two thirds of publicly reported outages were caused by third-party providers, such as cloud, network operators or data centres. In this year’s survey, 57% of respondents said their most recent serious outage cost more than $100,000, and one in five put it at over a million14.
See the common thread? The customers of those companies did nothing wrong. They depended on a single provider, and that provider had a bad day.
BLIK has bad days too
In Poland, the provider people notice most is payments. According to Gemius, 72% of online shoppers pay with BLIK, the Polish mobile payment system, and 82% shop mainly on a smartphone15. For many stores BLIK simply is the till.
On the morning of 1 November 2025 BLIK codes could not be generated. On 3 November the problems returned, the operator confirmed an external DDoS attack, which floods servers with fake traffic, and payments struggled for around four hours16. On 10 June 2026 Pekao bank customers could not pay with BLIK or confirm online payments from the early morning17.
Think about what that means for a store whose checkout offers only BLIK through a single payment gateway. Customers won’t wait four hours. They will go where they can pay by card or instant transfer.
Ransomware goes for your backups first
The most dangerous attacks, though, target the business itself. CERT Polska recorded 179 ransomware attacks in 2025, malware that encrypts data and demands a ransom. That is a record. In 46 cases the attackers got in through a remote desktop exposed to the internet18.
What strikes me most is another part of the report. Attackers deliberately look for backup servers. Backups kept on network drives in the office get wiped, and virtual machine snapshots get deleted, before encryption begins18. A backup reachable from the same account as the store is lost together with it.
Veeam’s survey of 1,300 organisations shows the result:
There has been a simple rule for backups for years. The US agency CISA describes it like this19:
Keep 3 copies of any important file: 1 primary and 2 backups. Keep the files on 2 different media types. Store 1 copy offsite. CISA, Data Backup Options
Today I would add one thing: at least one copy must be out of reach of the accounts you use to run the store, and you need to rehearse the restore before you need it.
A business continuity plan in five steps
A business continuity plan sounds like paperwork for a bank. For an online store, a few pages and a few decisions made in a calm week are enough:
- List what sales depend on. Hosting, domain, DNS, payment gateways, couriers, ERP, marketplaces. For each one, note who has access to the account and how to reach the provider during an outage.
- Keep backups by the 3-2-1 rule. One copy off-site and out of reach of everyday accounts. Every so often, restore the store from a backup onto a separate server and time it19.
- Have a second way to pay. When BLIK or your main gateway is down, customers should be able to pay by card or instant transfer through another operator16.
- Plan your exit from each provider. Since 12 September 2025 the EU Data Act has given you the right to switch cloud providers, and from 12 January 2027 it bans charging for it9. The stores that benefit are those whose setup is documented and can be rebuilt with another provider.
- Keep a regulation calendar. Write down the KSeF, NIS2 and accessibility deadlines and prepare changes early, with room for postponements5,6.
I would add one more dependency to the list, one people rarely mention: your developer. A store that only one person or one agency understands has a single point of failure in its people. We wrote about this when discussing switching e-commerce agencies.
How we work
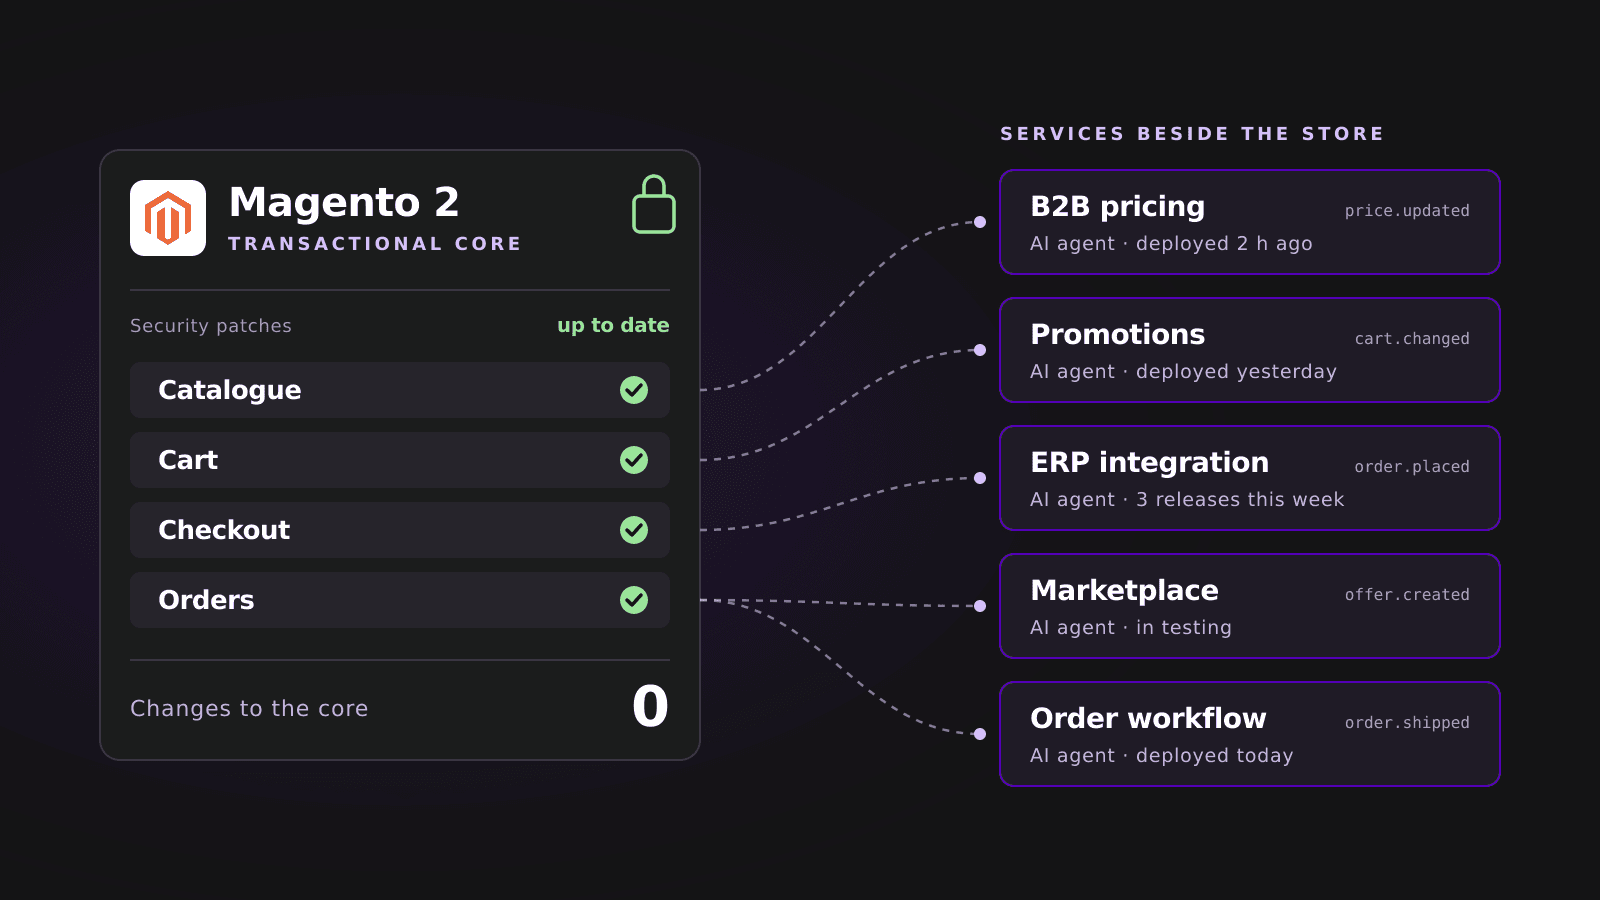
At WEGOTCOOKIES we look after stores after launch too. We install security patches before anyone finds the hole, keep Magento, PHP and modules up to date, and review performance and errors before customers notice them. When something breaks at night, we don’t leave you to deal with it alone. The longest we have looked after a single project is more than 10 years.
We write code as if someone else will read it tomorrow, and we also take over stores from other developers. Read more about how we work on our about page, and about connecting a store to company systems on the ERP and CRM integrations page.
If you remember one thing from this post, let it be this: you have no influence over what happens in the Tribunal or in Amazon’s data centre. Whether your store depends on a single provider or a single person is entirely up to you.